
Modernize Your Policy to Cover Fines and Investigations Under GDPR, CCPA & More
A high-profile breach like the Cloudflare incident guarantees one thing: regulatory scrutiny. But many older cyber policies were written before modern privacy laws like GDPR existed. Their definitions of a “claim” or “wrongful act” are dangerously outdated, leaving you exposed to massive legal bills and insurable fines.
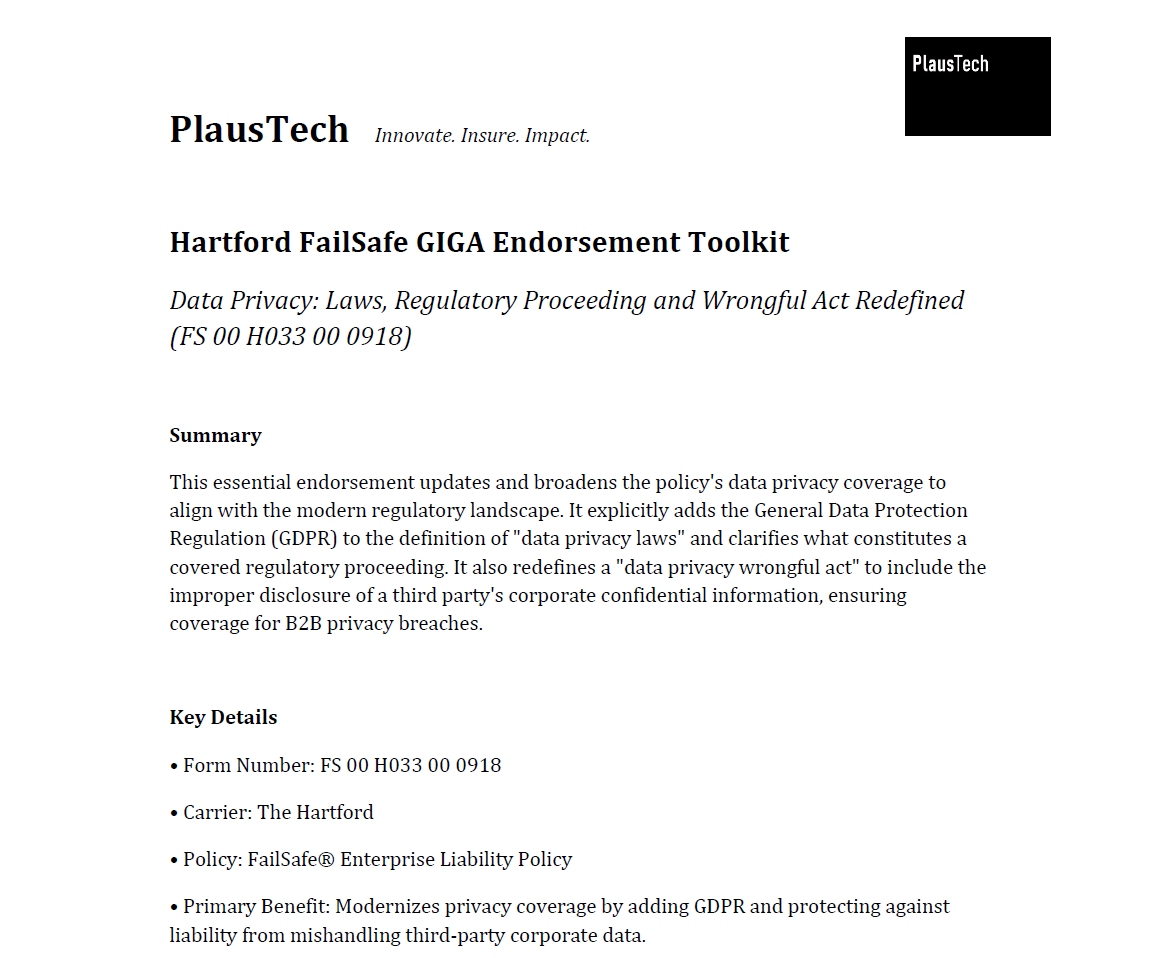
This free resource provides the full Hartford FailSafe GIGA endorsement that modernizes your policy for today’s regulatory landscape.
Why Download This Endorsement?
Regulatory defense costs can be as crippling as the breach itself. This language updates your policy’s core definitions to trigger coverage. Use this form to find out:
✔️ How “Wrongful Act” is redefined to explicitly include violations of data privacy laws.
✔️ If the policy will pay for legal expenses to respond to informal inquiries, not just formal lawsuits.
✔️ Which specific types of regulatory proceedings, fines, and penalties are covered.
Ensure your policy is ready for the inevitable call from regulators. This document shows you what true “state-of-the-art” coverage looks like.
Get Instant Access Now
Simply fill out the form below to download the PDF instantly — no waiting for email, no strings attached.
What Happens Next: After you hit ‘Submit,’ you’ll be taken directly to a page to download this endorsement. On that page, you’ll also get instant, one-click access to the complete Hartford FailSafe GIGA Supply Chain Toolkit, including the base policy form and 6 other critical endorsements discussed in our article.
We respect your privacy and will not share your information with third parties.